KMS now supports asymmetric encryption and digital signatures
October 7, 2026
SecurityKMSEncryption
Exoscale Key Management Service (KMS) now supports asymmetric keys for encryption and digital signatures. They’re available through the API, CLI, Portal and SDKs.
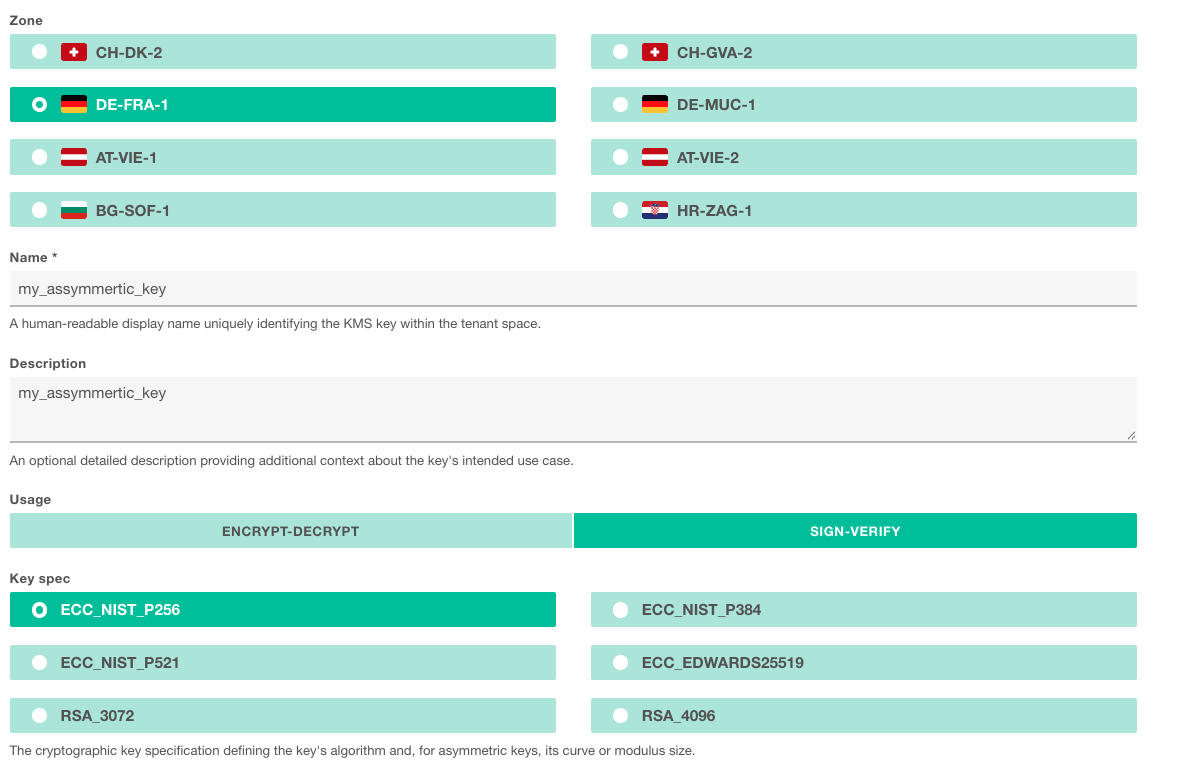
What’s new
- RSA encryption: Create RSA-3072 or RSA-4096 key pairs and export the public key to whoever needs to send you data. They can encrypt without a KMS account, and decryption happens only inside KMS, with the private key never leaving it.
- Digital signatures: Sign data with RSA-PSS, ECDSA, Ed25519 or ML-DSA keys. Signing always happens in KMS. You can verify signatures in KMS as well, or export the public key and verify with your own tools, offline if needed.
- Post-quantum signatures: ML-DSA-65 and ML-DSA-87 implement FIPS 204, the Module-Lattice-Based Digital Signature standard NIST published in 2024. Unlike RSA and ECDSA, ML-DSA is designed to resist forgery by future quantum computers. That makes it a fit for signatures that must remain verifiable for many years. ML-DSA-65 targets NIST security category 3, and ML-DSA-87 targets category 5.
These additions let you use KMS for application encryption, signing workflows, and integrations that require public-key cryptography, without exposing private key material.

